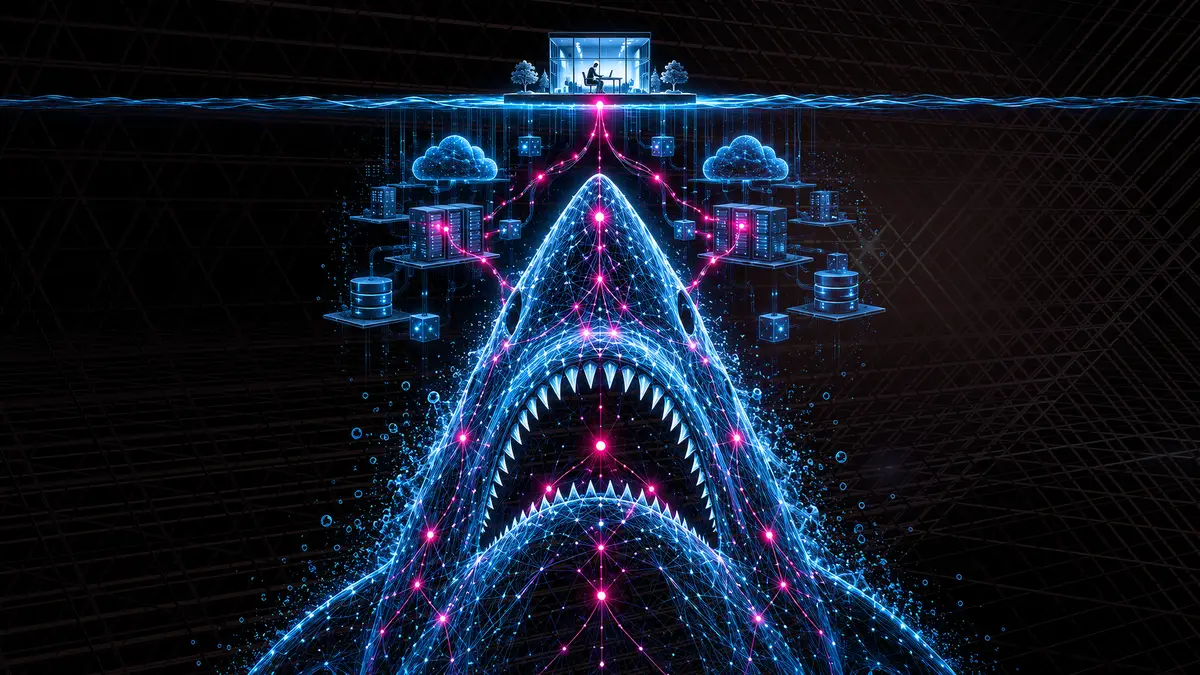

What lies beneath: making sense of the PHP cyber panic
Two critical vulnerabilities in PHP triggered global warnings in October. Headlines described a threat affecting 70 per cent of the internet and raised the prospect of attackers taking remote control of websites.
The underlying risk was serious. Flaws in PHP2Shell were uncovered by researchers who demonstrated that an unauthenticated attacker could read sensitive process memory or execute code remotely under certain conditions.12 This would allow hackers to leverage compromised servers to run their instructions - potentially leading to stolen credentials, altered website content, installation of malware and mass leaks of customer data.
What is PHP and why this matters for you
PHP is a programming language that runs on a web server. When a visitor requests a page, PHP can retrieve information from a database, process a form, check a login, assemble a page and send the result back to the browser.
WordPress is written largely in PHP. So are Drupal, Joomla and many custom business applications. WordPress plugins and themes also commonly contain PHP code.
PHP lies beneath the part of WordPress that most business owners see. A WordPress dashboard may show that the core system and plugins are current while the PHP runtime on the server remains the responsibility of a hosting company, systems administrator or developer. Updating WordPress alone does not update PHP.
Platforms like Shopify do not run on PHP themselves, but businesses using them can still be exposed through third-party apps, where PHP code is hosted on developer servers and connected into online stores.3 The app provider's server and maintenance practices become part of the store's supply chain and expose the store owner to unexpected risk.
Why WordPress is the main exposure for Wallace clients
For Wallace Corporation clients, the most common direct PHP exposure is a self-hosted WordPress website.
The PHP2Shell flaws sat in PHP itself. They did not require a vulnerable WordPress plugin, and even a minimal PHP application could be affected.2 A large plugin stack therefore did not cause this particular vulnerability.
Plugin-heavy sites still carry more risk overall. Every plugin adds code, update cycles, supplier decisions and possible incompatibilities. More dependencies also make emergency runtime upgrades harder to test. A lean WordPress site with controlled dependencies has a smaller attack surface and a simpler recovery path, although it still requires active PHP, WordPress, theme and plugin maintenance.
This is the same maintenance boundary Wallace Corporation raised with clients in August. WordPress remains a capable publishing platform, but its security depends on several layers working together: the hosting environment, PHP, WordPress core, themes, plugins, user accounts, external services, monitoring and recovery.
What security measures we've taken for our clients
Wallace Corporation treated the disclosure as an infrastructure event rather than waiting for a routine website update.
- Server access was restricted immediately while exposure and patch availability were assessed.
- Patched PHP versions were applied as soon as they became available.
- WordPress sites covered by active maintenance plans were scanned.
- WordPress core, plugins and themes were reviewed and updated for maintained clients.
The distinction between hosting and maintenance matters. Hosting keeps a website available. Active maintenance assigns responsibility for reviewing alerts, applying updates, checking the wider software stack and investigating signs of compromise. For clients without active maintenance plans this particular vulnerability has been patched indirectly through our server updates. However it is highly probable that your WordPress version is out of date leaving your website vulnerable to other forms of attack.
We are asking clients to seriously consider whether WordPress remains the right platform for their business.
Alastair McLeod, Founder, Wallace Corporation
AI is changing the risk equation
The flaws behind PHP2Shell had existed for more than a decade. The difficult part was turning subtle memory errors into a working attack across different versions, configurations and applications.
AI reduces the amount of highly specialised labour required for that work. A capable model can read a large codebase, explain unfamiliar components, propose ways to combine several weaknesses, write tests, examine failed attempts and adjust an exploit for another configuration. Those tasks still require tools, access and human judgement, but they can be repeated much faster and at much greater scale.
OpenAI CEO Sam Altman described the broader problem directly: “AI will be incredibly good at finding vulnerabilities in software. And I think the world will find that their software is much more brittle and much less secure than we thought.”4
The same capability helps defenders. Raluca Ada Popa, Head of Gemini Security at Google DeepMind, said the PHP2Shell work showed why “frontier AI is a game-changer for cyber defense”, after models helped researchers find the vulnerabilities and validate the patch.2
That defensive advantage depends on speed. OpenAI expects similar findings to increase sharply and has warned that the same capabilities can help attackers develop offensive tools and exploits.5 Australian Signals Directorate's 2025-26 threat report reached a similar conclusion: AI is reducing the expertise and effort needed to identify and exploit vulnerabilities, shortening the time available to patch.6
Security patching has accelerated sharply in 2026
Official WordPress security notices show an uneven history rather than a steady year-on-year increase. Our count of core security release events is shown below, with a sharp change in 2026. This is the operational reality of maintaining a platform built upon several independently moving layers.
Security release events by year
View the chart data
| Year | Security release events |
|---|---|
| 2022 | 4 |
| 2023 | 4 |
| 2024 | 3 |
| 2025 | 1 |
| 2026 to 28 October | 9 |
What this means for Australian businesses
The Australian Signals Directorate's Australian Cyber Security Centre received more than 82,000 cybercrime reports in 2025-26, an average of one report every six minutes. Businesses reported an average self-reported loss of $93,500 per cybercrime report, up 16 per cent from the previous year. 6
These figures show why a website incident cannot be treated solely as a technical inconvenience. A compromised site can expose customer information, interrupt sales and enquiries, damage trust, trigger investigation costs and create legal obligations. In our experience, almost all small business owners have little to no understanding of these risks and the potentially devastating impacts a cybersecurity incident can have.
Practical next steps for any business
- Identify who is responsible. Name the person or provider responsible for hosting, PHP, WordPress and security alerts. Record who must act and how to contact them.
- Confirm everything is patched and current. Check that the PHP2Shell update has been applied, then confirm the versions of WordPress core, themes and plugins are supported and up to date.
- Put active WordPress maintenance in place. Assign ongoing responsibility for updates, security reviews, monitoring and incident response. Hosting alone does not cover this work.
- Remove unused code. Delete plugins, themes, apps, integrations and administrator accounts that are no longer required.
- Set up two-factor authentication. Protect WordPress administration, hosting, domain, email and other important accounts with a second login check.
- Confirm backups work. Keep a recent backup outside the live website and test that it can be restored.
- Understand the legal obligations. Know what personal information the website holds, when evidence must be preserved, and when a breach may need to be reported or communicated.
- Audit whether the platform is still appropriate. Review its dependencies, maintenance load and recovery options, then decide whether it remains suitable and resilient as security risks and patching demands increase.
What lies beneath?
The PHP2Shell vulnerability has been discovered by security researchers with an interest in protecting the digital world from widespread hacks. The industry is making it clear that this is only the beginning and other vulnerabilities will follow.
It is now critical for business owners to understand what lies underneath their tech stack and digital presence, to know what risks they face and how to manage any emergency situations. The benefits of legacy platforms must outweigh the increasing maintenance burden and wherever feasible business owners should consider migrating to future-proof, low exposure platforms to successfully weather future online storms.
References
- Cybersecurity and Infrastructure Security Agency, “Critical Vulnerabilities in PHP Require Immediate Patching”, revised 26 October 2026.
- Wiz Research, “PHP2Shell: AI uncovers critical RCE vulnerabilities affecting 70% of the Internet”, 21 October 2026.
- Shopify Developer Documentation, “Libraries and templates”, accessed 30 October 2026.
- OpenAI Forum, “Event Replay: Sam Altman on Building the Future of AI”, transcript at 00:13:26, 6 April 2026.
- OpenAI, “Patch the Planet: global response coordination as agents uncover critical vulnerabilities”, 21 October 2026.
- Australian Signals Directorate's Australian Cyber Security Centre, “Annual Cyber Threat Report 2025-26: Year in Review”, October 2026.
- WordPress.org, “Releases” archive, reviewed through 28 October 2026.
TL:DR - Key Statistics
2 critical
PHP vulnerabilities leading to emergency patches across the internet
> 10 years
the vulnerable code survived before AI helped turn it into working exploits
9 security updates
for WordPress in 2026 to date, compared to only 1 in 2025 and 3 in 2024.
$93,500
average loss to Australian businesses due to cybercrime in 2025-26.
Featured
Web Development Mornington Peninsula | Wallace Corporation
Rosebud-based web development for Mornington Peninsula businesses. Focused websites, e-commerce and custom systems, scop…
EXPLORE →Conversational AI Voice Agents
Never miss another inbound lead with 24/7 AI voice agents.
LEARN MORE →Lessons learned spending 4 billion tokens on a new website with AI agents
We've rebuilt our website as a database-backed business platform. The project used nearly 4 billion input tokens & appro…
READ ARTICLE →Voice agent readiness: building modern customer service systems
Voice AI needs clean customer data, controlled access & reliable hand-off. Voice Agents are coming to our phone lines, i…
READ ARTICLE →Find out what is running underneath your website
Wallace Corporation can identify the platform, runtime and maintenance responsibilities behind an existing website, then advise whether it should be patched, actively maintained or replaced with a smaller platform.